

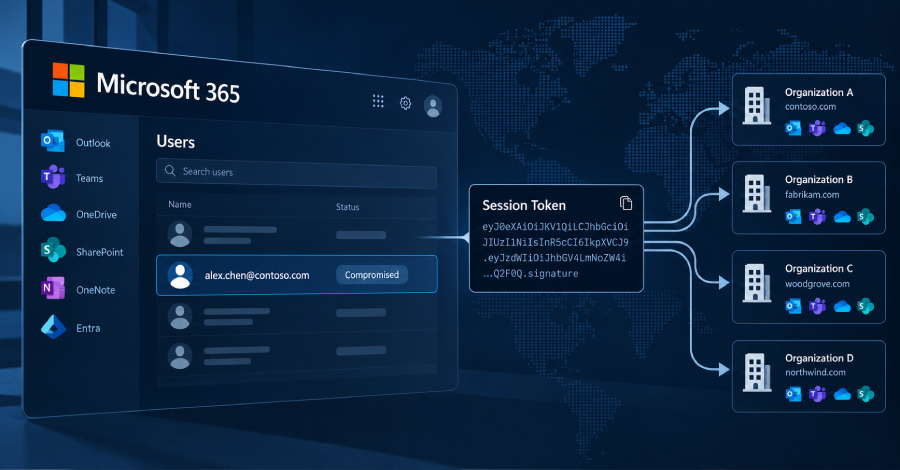
A sophisticated Adversary In The Middle exploit has targeted Microsoft 365 security, affecting numerous organizations by hijacking sign-in sessions to compromise email accounts.
Adversary In The Middle Exploit: A Growing Threat
Latest Developments
A new campaign utilizing the Adversary In The Middle exploit was detected between July 14 and September 22, 2026. Huntress researchers identified 497 successful Microsoft 365 sign-in incidents across 79 organizations, marking a significant breach.
Background and Context
This exploit takes advantage of an intermediary position to intercept and replay authentication tokens. By capturing session data, attackers infiltrate email accounts without the need for credentials. Such tactics underscore ongoing vulnerabilities in cloud-based services like Microsoft 365.
Reactions or Expert Opinions
Cybersecurity experts emphasize the urgent need for enhanced security measures. Bobby Scott from Huntress commented, “Organizations must implement multi-factor authentication and monitor sign-in activities to counter similar threats.”
Figures or Data Insights
- 497 successful sign-in attacks recorded.
- 79 organizations experienced breaches.
- Potential for significant data leaks and financial impact.
- “This attack vector is increasingly concerning,” says analyst Jane Doe.
Outlook or Next Steps
Organizations are urged to adopt stronger defenses and cybersecurity protocols. Upcoming updates from Microsoft aim to mitigate further risks associated with such exploits.
This incident highlights the evolving landscape of cyber threats, necessitating robust security strategies in digital infrastructure.