

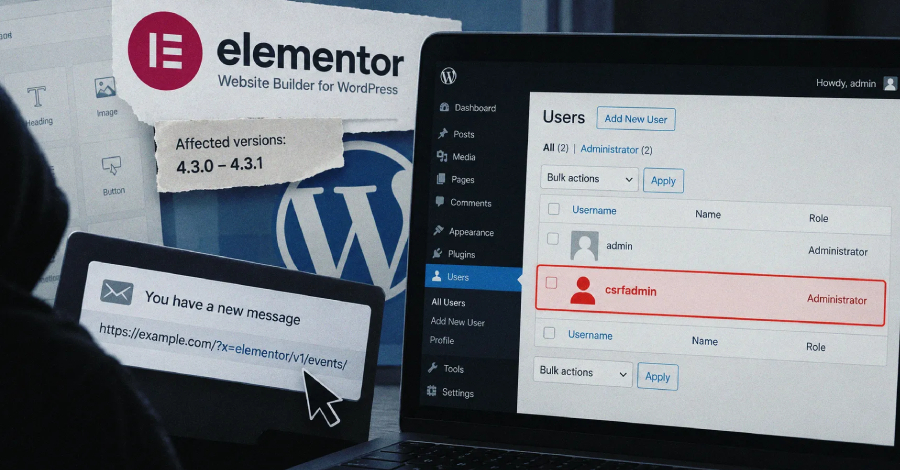
The recent discovery of an Elementor Plugin CSRF Vulnerability Exploitation has raised concerns among website administrators. This high-severity security flaw in the Elementor Website Builder WordPress plugin could allow attackers to create rogue admin accounts.
Elementor Plugin CSRF Vulnerability Exploitation
Latest Developments
A cross-site request forgery (CSRF) vulnerability has been identified. It remains unassigned with a CVE identifier. Scoring 8.8 out of 10 on the CVSS scale, it poses significant risks, primarily affecting plugin versions not yet specified. Administrators are urged to stay vigilant.
Background and Context
Elementor is a popular website building tool for WordPress. The recent flaw allows unauthorized account creation, threatening site security. CSRF vulnerabilities exploit the trust a website has in a user’s browser, leading to unauthorized actions. The issue has intensified the call for robust security measures.
Reactions or Expert Opinions
Security experts emphasize the need for immediate action. “Admins must update and monitor their systems,” one analyst noted. Many argue that regular security assessments could prevent such exploitation. These insights underline the necessity of proactive defenses.
Figures or Data Insights
- CVSS score: 8.8 out of 10
- Potential impact on millions of WordPress sites
- Growing trend of plugin vulnerabilities
- “Prompt updates can thwart potential threats,” a security expert advised
Outlook or Next Steps
Administrators should prioritize updates and security patches. This proactive approach could mitigate risks posed by the vulnerability. Keeping abreast of security advisories is crucial. As threats evolve, preparedness remains key to safeguarding websites.
This development highlights broader concerns about plugin security in content management systems. Staying informed and responsive is vital as the digital landscape continues to evolve.